- Securitylinkedin.com
VPN Provider Surfshark Discloses Breach of Internal Testing and Proxy Infrastructure - LinkedIn
Surfshark revealed a breach of an internet-exposed testing server and an isolated proxy system due to a misconfigured internal test server, allowing unauthorized access to limited engineering material…
- ibtimes.sg
LinkedIn Has Had Enough of AI Slop; 1 Million Users Agree
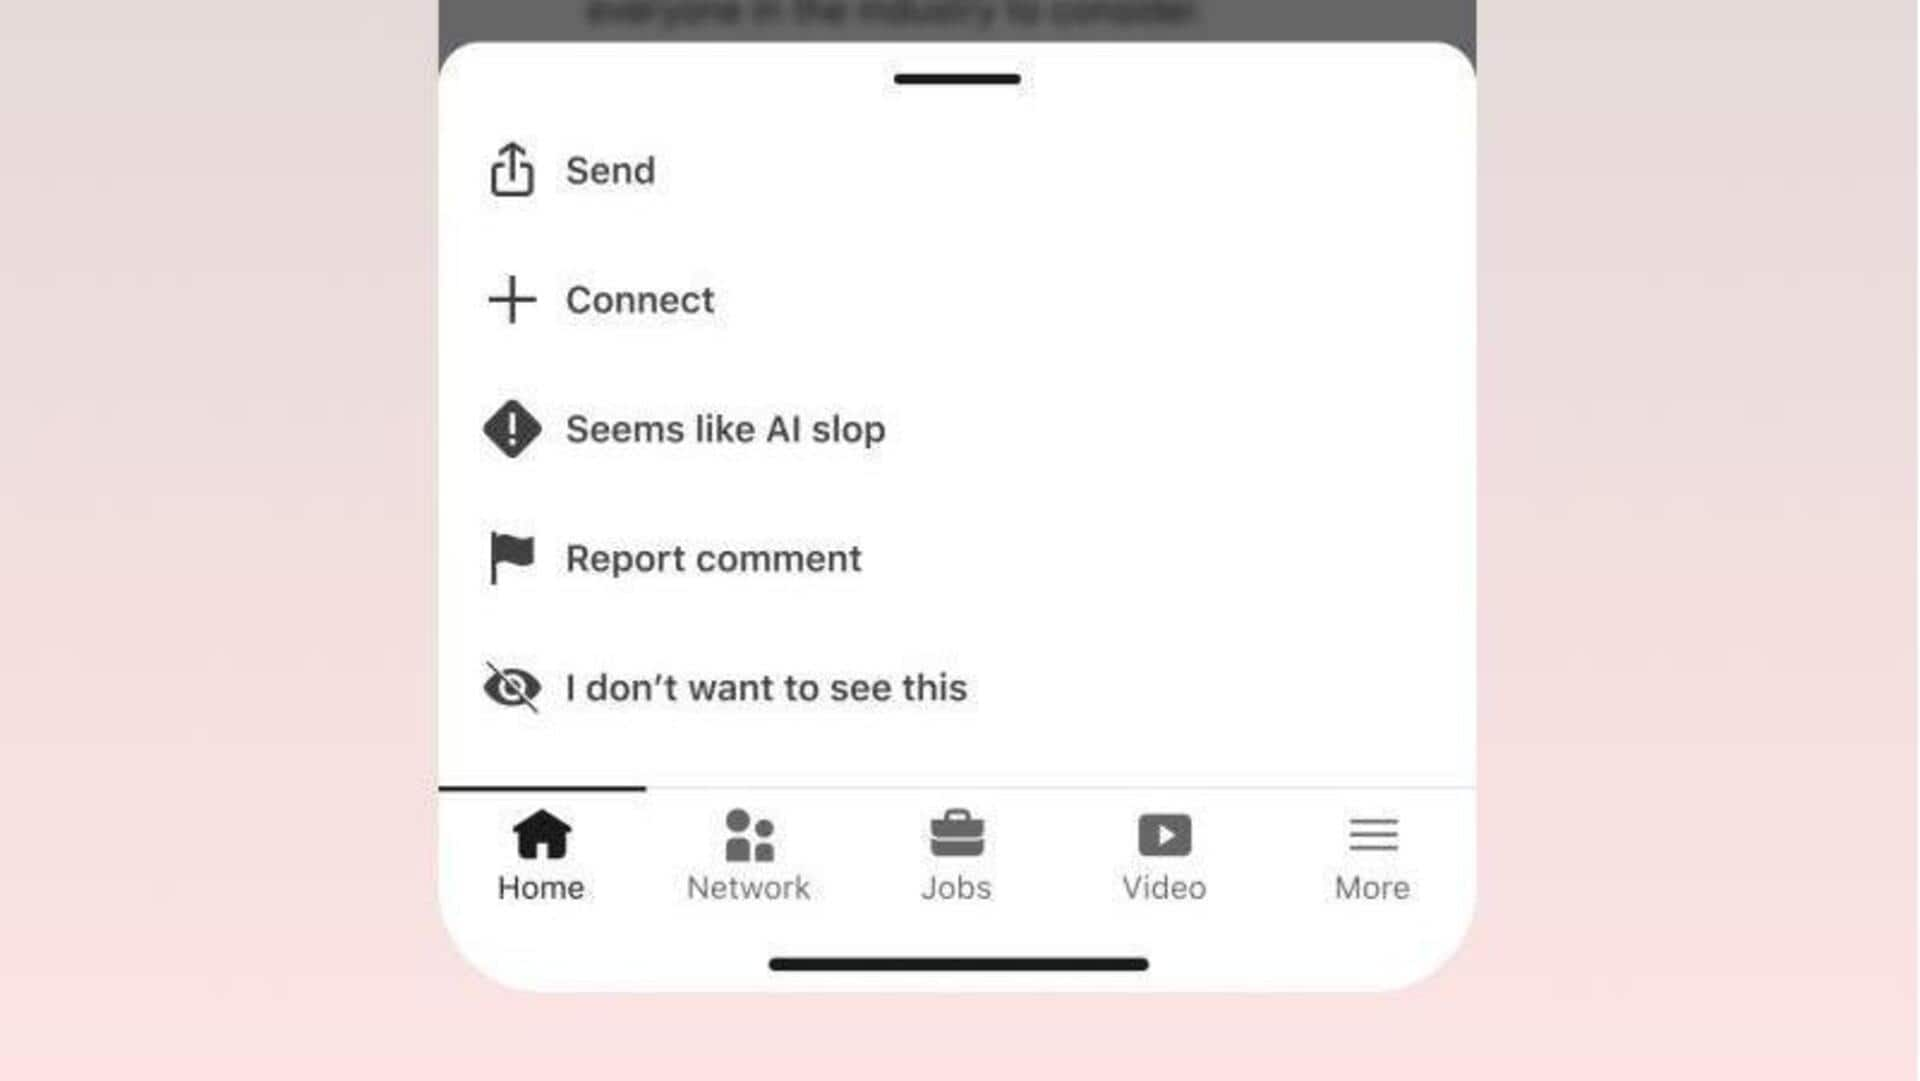
LinkedIn introduced a 'Seems like AI slop' reporting tool on July 30, which has been used over 1 million times. The platform now sees a 40% reduction in views for content classified as AI slop, using …
- Fundinglinkedin.com
ESDS Software Solution IPO | India’s First Listed Data Centre Play? | Piyush Somani Exclusive - LinkedIn
ESDS Software Solution announced a ₹720 crore IPO, positioning itself as India’s first listed data centre and cloud infrastructure player. The company’s business spans cloud infrastructure, GPU-as-a-S…
- Featurecybernews.com
LinkedIn “AI Slop” button clicked over 1M times since release
LinkedIn added a 'seems like AI Slop' button allowing users to flag potentially AI-generated posts, with over 1 million clicks in two weeks. The feature provides post analytics showing how many users …
- medianama.com
How does LinkedIn distinguish “AI slop” from AI-assisted writing?
LinkedIn’s ‘Seems like AI slop’ reporting option for posts and comments has surpassed one million clicks, according to Chief Product Officer Hari Srinivasan. The feature aims to identify low-effort, l…

- newsbytesapp.com
1M+ users have used LinkedIn's 'AI slop' button
LinkedIn’s 'AI slop' button, introduced to flag AI-generated content, has been used by over a million users since its July 30 launch. The feature, part of a broader effort to address AI slop, includes…
- startupfortune.com
LinkedIn Users Click Its AI Slop Reporting Button a Million Times
LinkedIn’s new 'seems like AI slop' button was clicked over a million times in its first two weeks, and posts flagged as low-substance AI content now receive 40% fewer views. The feature follows resea…

- theverge.com
Over 1 million people have clicked LinkedIn’s AI slop button
LinkedIn’s new 'Seems like AI slop' button, introduced July 30, has been clicked over 1 million times. The feature, part of efforts to combat AI-generated content, now shows users a message if their p…

- Securitylinkedin.com
Microsoft Confirms Maximum-Severity Entra ID Vulnerability Exploited In Attacks - LinkedIn
Microsoft disclosed CVE-2026-69836, a CVSS 10.0 vulnerability in Entra ID (Azure AD) involving deserialization of untrusted data, allowing remote code execution without prior privileges. Exploitation …
- Securitylinkedin.com
Hacker Claims To Have Stolen 3.6 Million Records From McDonald’s, Vodafone and Other Corporate Azure Tenants - LinkedIn
A threat actor named TheHatman is attempting to sell 3.64 million records allegedly stolen from Microsoft Entra ID environments of nine major companies, including McDonald’s, TCS, and Vodafone. Sample…
- Securitylinkedin.com
Microsoft’s August 2026 Patch Tuesday Fixes 400+ Vulnerabilities - LinkedIn
Microsoft’s August 2026 Patch Tuesday addressed over 400 vulnerabilities, including three zero-days—one actively exploited by the North Korean Lazarus group via a Windows kernel flaw (CVE-2026-68820).…
- Featureforbes.com
What LinkedIn's AI Slop Crackdown Means For Your Posts
LinkedIn introduced a new 'AI slop' reporting button to flag AI-generated posts and comments, with over 40% of long-form posts on the platform now fully AI-generated. Posts flagged as AI slop face red…

- Securitylinkedin.com
New Passkey Attacks Expose Private Keys and Bypass Phishing-Resistant MFA Without Breaking Encryption - LinkedIn
Three independent security investigations revealed weaknesses in passkey systems, allowing attackers with endpoint access to impersonate users, bypass phishing-resistant MFA, or recover private keys. …
- Securitylinkedin.com
Google Patches Sixth Chrome Zero-Day of 2026 As V8 Flaw Comes Under Active Attack - LinkedIn
Google issued an urgent Chrome 152 update to fix CVE-2026-85046, a high-severity type-confusion flaw in the V8 engine under active attack. The vulnerability allows remote code execution in Chrome’s sa…
- afr.com
LinkedIn lets users red flag avalanche of AI slop
LinkedIn introduced a feature allowing Australian users to flag low-effort, likely AI-generated content as 'AI slop' using a dedicated button. The move follows Substack's recent AI detection tool and …
- hrdive.com
LinkedIn offers the option to report AI slop
LinkedIn is testing a feature allowing users to privately flag posts or comments suspected to be AI-generated ('AI slop') via a three-dot menu. The platform will use these reports to refine its detect…

- Featureforbes.com
LinkedIn Just Changed The Rules. Here's How To Stay Visible
LinkedIn reversed its AI-first content strategy after AI-generated posts caused a 56% drop in engagement and a trust crisis. The platform now reduces visibility of generic AI content, introduces a fla…

LinkedIn 在 2026年8月 发布了 17 项受追踪的更新。 较 2026年7月 增长 240%。 主要主题是 security incidents(6)。 活动主要集中在 2026年8月17日 那一周。 亮点:“VPN Provider Surfshark Discloses Breach of Internal Testing and Proxy Infrastructure - LinkedIn”(2026年8月31日)。
信号分类:2026年8月
6
security incidents
3
feature updates
1
funding events
浏览 LinkedIn 的其他月份